Certificate of Networthiness Complete Guide to Software Security Approval
Certificate of Networthiness
Old software records often mention a “CoN.” Many readers do not know what it means. Some think it is a modern security badge. It is not.
This guide explains the Certificate of Networthiness in plain words. You will learn what it was, why the Army used it, and how it differs from newer approvals.
What Is a Certificate of Networthiness?
A Certificate of Networthiness (CoN) was a U.S. Army software approval. The Army used it to check whether an application could run on its enterprise networks.
Reviewers looked at four main areas: security, compatibility, supportability, and sustainability.
You may still see the term in old contracts, technical files, and compliance papers. Treat it as a past Army approval. It is not a general cybersecurity certificate for every company.
What Does CoN Mean?
CoN stands for Certificate of Networthiness.
The certificate covered software and its tested setup. It did not cover a person, a website, or an employee.
Old records show what a CoN could list:
- The product name
- The software version
- The tested configuration
- The certificate number
- The approval date
- The end date
Some records also said that big software changes needed a new review.
Why Did the Army Use It?
The Army needed control over the software on its networks. Unchecked software can bring risks. It may create security gaps. Clash with other systems. It may also be hard to maintain.
A review helped the Army catch these problems early. Company announcements from that time also called the CoN. Army and Department of Defense software approval.
What Did Reviewers Check?
The exact rules changed from one application to another. Still, most reviews looked at these areas:
- Security: Reviewers checked security controls and possible risks.
- Compatibility: The software had to work with the planned technical setup.
- Supportability: The Army needed a practical way to maintain the software.
- Sustainability: The product had to stay manageable over time.
- Configuration: The approval covered one tested version and setup. It did not always cover future versions.
A software change could affect the approval. A new version often meant a new look.
How Did the Process Work?
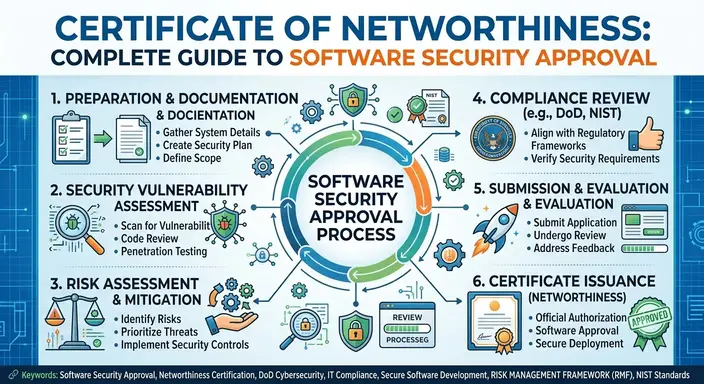
The workflow varied. Still, most cases followed five broad stages:
- Application details: The software owner shared product and technical facts.
- Technical review: Reviewers studied how the software worked in the planned setup.
- Security check: Reviewers weighed the security risks and controls.
- Compatibility check: Teams looked at network, operating system, and setup needs.
- Decision: The authority could approve the software. add conditions, ask for changes, or say no.
Old Army records show that a decision could include limits. Some approvals fit only one configuration.
Did a CoN Mean the Software Was Fully Safe?
No. A CoN was not a lifetime promise of safety.
It showed an assessment. That assessment covered one set of rules, one setup, and one date.
Software changes over time. New flaws appear. This is why modern security teams manage risk all the time. They do not trust one old certificate forever.
CoN vs. a General Cybersecurity Certificate
| Point | CoN General Cybersecurity Certificate |
|---|---|
| Origin | Past U.S. Army software approval |
| Focus | Software in Army networks |
| Scope | One product version or setup |
CoN vs. Authority to Operate
A CoN and an Authority to Operate (ATO) are not the same thing. They come from different approval ideas. Their scope can differ too.
Does your defense project mention CoN, ATO, RMF, or another approval? Then follow the current rules of the responsible group. Do not rely on an old article or an old certificate alone.
Is the CoN Still Required Today?
Today, people mostly see the term in old or legacy records.
The Army published a revised regulation in 2019. It removed the Certificate of Networthiness and several older cybersecurity rules. It pointed readers to newer cybersecurity guidance.
So do not assume an old CoN rule fits a new Army project. Follow the Army and Department of Defense rules that apply today.
Who Used the CoN?
The term belonged to U.S. Army and related Department of Defense networks. Old records also mention the National Guard and Army Reserve. These groups used Army enterprise systems.
Why Do Old CoN Records Still Matter?
Old records still help when a team maintains older software. They can show:
- Which version received approval
- Which setup the approval covered
- When the approval started and ended
- Which limits applied
- Why a later update may need a new review
Army support records say a certificate could become invalid after a major setup change. An upgrade could also call for a new check.
A Simple Example
Imagine a team finds an old CoN for a software tool. The certificate lists version 3.0.
Now the team runs version 5.0. Can it use the old certificate as proof of approval? No. The old paper covers only version 3.0.
The team must check the current rules. It may need a fresh review.
Tips for Handling Old CoN Records
- Read the version. Match it to the software you use now.
- Check the dates. Look for end notes.
- Note the limits. Find any conditions listed on the record.
- Check today’s rules. Ask the responsible authority what applies now.
- Keep records safe. Old files help during audits and upgrades.
Common Mistakes
Treating a CoN as a person’s credential. It covered software only.
Using an old CoN as current proof. Rules have changed.
Ignoring version changes. A new version may need a new review.
Mixing up CoN and ATO. They are different approvals.
Believing a CoN meant zero risk. No approval removes every risk.
Frequently Asked Questions
What does Certificate of Networthiness mean?
It was a U.S. Army approval process. It checked whether software could run on Army enterprise networks.
Who used the CoN?
U.S. Army and related Department of Defense networks used it. Army Reserve and National Guard users also worked in Army systems.
Does a CoN certify a person?
No. It covered software and its tested setup. It was not a professional credential.
Can a software update affect a CoN?
Yes. Old records show that big setup changes and new versions could need a new review.
Can I use an old CoN as proof of current compliance?
Not by itself. Current compliance depends on today’s rules. Your software version, your setup, and the approval process in force now.
Is a CoN the same as an ATO?
No. They are different approvals with different scope.
Conclusion
The Certificate of Networthiness was a past U.S. Army software approval. It checked security. Compatibility, supportability, and related needs before software ran on Army networks.
The term still appears in legacy records. It helps you read old files. But do not confuse an old CoN with a lifetime or universal security certificate.
For any current defense or government project, check the latest rules. Ask the responsible authority. Then follow today’s cybersecurity approval steps.